TLDR: To set up DKIM, generate a public and private key pair, publish the public key as a DNS record at selector._domainkey.yourdomain.com, turn on signing in your email platform, and send a test message to confirm it passes. Most providers generate the keys for you, so the real work is adding the record to DNS correctly.
DomainKeys Identified Mail (DKIM) is a digital signature for your email. It tells receiving servers that a message really came from your domain and that nobody changed it along the way.
Setting it up used to be optional. Today, Gmail, Yahoo Mail, and Microsoft all require DKIM from bulk senders, and a missing or broken signature is one of the fastest ways to the spam folder. DKIM is also only as good as its setup.
The setup takes five steps, and most failures come down to a small mistake in a DNS record. Below, we’ll walk through the process, show where it differs on Google Workspace and Microsoft 365, and cover the mistakes behind most failed setups.
What is DKIM (and how does it work)?
DKIM is an email authentication method that lets a receiving server verify two things: The message was authorized by the domain in its signature, and its contents weren’t altered in transit. DKIM doesn’t encrypt your message. It works more like a tamper-evident seal.
It relies on a pair of keys:
- The signature: Your sending server uses a private key to add an encrypted signature to each message’s header.
- The public key: You publish the matching public key in your domain’s DNS, where any server can look it up.
- The verification: The receiving server reads the signature, fetches your public key, and checks that the two match.
- The result: A match means the message passes DKIM. A mismatch means it fails, and the message may be filtered or rejected.
For the full explanation, see our guide to DKIM.
Before you set up DKIM
Before setting up your DKIM, it’s a good idea to do a little planning. This will set you up for success (and maybe prevent you from duplicating efforts).
Check if DKIM is already set up
You might already have it. Many email providers turn DKIM on by default or set it up during onboarding. Valimail’s free DKIM checker pulls up your record instantly. You can also check by hand:
- Send a test message to a Gmail account.
- Open it, click the three-dot menu next to the reply button, and select “Show original.”
- Find the DKIM line. If it says “PASS” next to your domain, DKIM is working.
Look closely at the domain on that line. If it shows your email provider’s domain, your messages are being signed with a default key, and you still need to set up DKIM for your own domain.
What you need before you start
Before we start, let’s make sure you have everything you need:
- Access to your domain’s DNS: You’ll add a TXT or CNAME record, so you need a login for your DNS host or a colleague who has one
- Admin access to your email platform: This is where you generate keys and turn on signing
- A list of every service that sends as your domain: Each one needs its own DKIM setup, including marketing, billing, and support platforms
- A selector name: A short label, such as s1 or google, that tells receiving servers which key to look up. Most platforms pick one for you, and our DKIM selector guide explains how they work.
If that list already looks long, Valimail Enforce automates DKIM and the rest of your email authentication across every sending service.
DKIM setup: Step-by-step process
1. Generate your DKIM key pair
First, you need to create your DKIM key pair. This consists of a private key (which your email server will use to sign messages) and a public key (which receiving servers will use to verify the signature).
- Use a DKIM key generation tool (many are available online)
- Choose a key size (2048 bits is more secure)
- Save both the private and public keys securely
2. Create your DKIM record
Now that you have your keys, it’s time to create your DKIM record. This is what you’ll add to your DNS.
- Start with your selector (a name for this particular key, like “mail” or “key1”)
- Add “._domainkey” to your selector
- Append your domain name
- Format your public key according to DKIM standards
Your record should look something like this:
mail._domainkey.yourdomain.com. IN TXT "v=DKIM1; k=rsa; p=MIGfMA0GCSqGSIb3DQEBAQUAA4GNADCBiQKBgQC3QEKyU1fSma0axspqYK49unoN..."3. Add the DKIM record to your DNS
Here’s how to do it:
- Log in to your DNS management interface
- Create a new TXT record
- Enter the DKIM record you created in the previous step
- Save your changes (and be patient — DNS changes can take up to 48 hours to propagate)
4. Configure your email server
Now, you need to tell your email server to start signing messages.
- Access your email server’s configuration
- Add your private key
- Configure your server to sign outgoing emails with DKIM
- Restart your email service to apply the changes
5. Test your DKIM setup
The moment of truth: let’s make sure everything is working.
- Send a test email to an external account (Gmail works well for this)
- View the email headers
- Look for the “DKIM-Signature” header and check if it passes
How to set up DKIM on Google Workspace, Microsoft 365, and ESPs
The five steps stay the same everywhere, but each platform puts them in a different place.
| Platform | Where to set it up | Record type | What you publish |
|---|---|---|---|
| Google Workspace | Admin console, under Gmail’s “Authenticate email” setting | TXT | One record at google._domainkey |
| Microsoft 365 | Microsoft Defender portal, under email authentication settings | CNAME | Two records: selector1._domainkey and selector2._domainkey |
| ESPs and marketing platforms | Domain authentication or sender settings | Usually CNAME | The records the platform generates |
| Your own mail server | Your signing software | TXT | The public key you generated |
Google Workspace DKIM setup
- In the Admin console, go to Apps > Google Workspace > Gmail > Authenticate email.
- Select your domain and click “Generate new record.” Choose a 2048-bit key and keep the default selector, google.
- Add the TXT record to your DNS.
- Return to the Admin console and click “Start authentication.”
Until you finish step 4, Google signs your messages with a default key on its own domain, which won’t align with yours. Google’s DKIM setup instructions have the full details.
Microsoft 365 DKIM setup
- In the Microsoft Defender portal, open the email authentication settings and select the DKIM tab.
- Choose your custom domain and select “Create DKIM keys.”
- Copy the two CNAME records Microsoft shows you, and add both to your DNS.
- Return to the DKIM tab and turn on signing for the domain.
Microsoft uses two selectors so it can rotate your keys automatically. See Microsoft’s DKIM configuration guide for the current record format.
ESPs and other sending platforms
Marketing, billing, and support platforms each sign with their own keys, so each needs its own records. Look for a setting named domain authentication, sender authentication, or sending domain. The platform will list the CNAME or TXT records to add. Publish them, then click verify.
Repeat this for every service that sends as your domain. Our guide to managing multiple DKIM records explains how they work side by side.
Automate your DKIM setup (and more) with Valimail
Setting up DKIM once is manageable. Keeping it right across a dozen sending services, with keys to rotate and vendors that change, is where teams fall behind. Valimail takes that work off your plate:
- Automated DKIM setup: Valimail generates your DKIM keys, creates the DNS records, and even helps with the email server configuration.
- DMARC management: DKIM is great, but it’s even better with DMARC. Valimail helps you implement and manage your DMARC policy alongside DKIM.
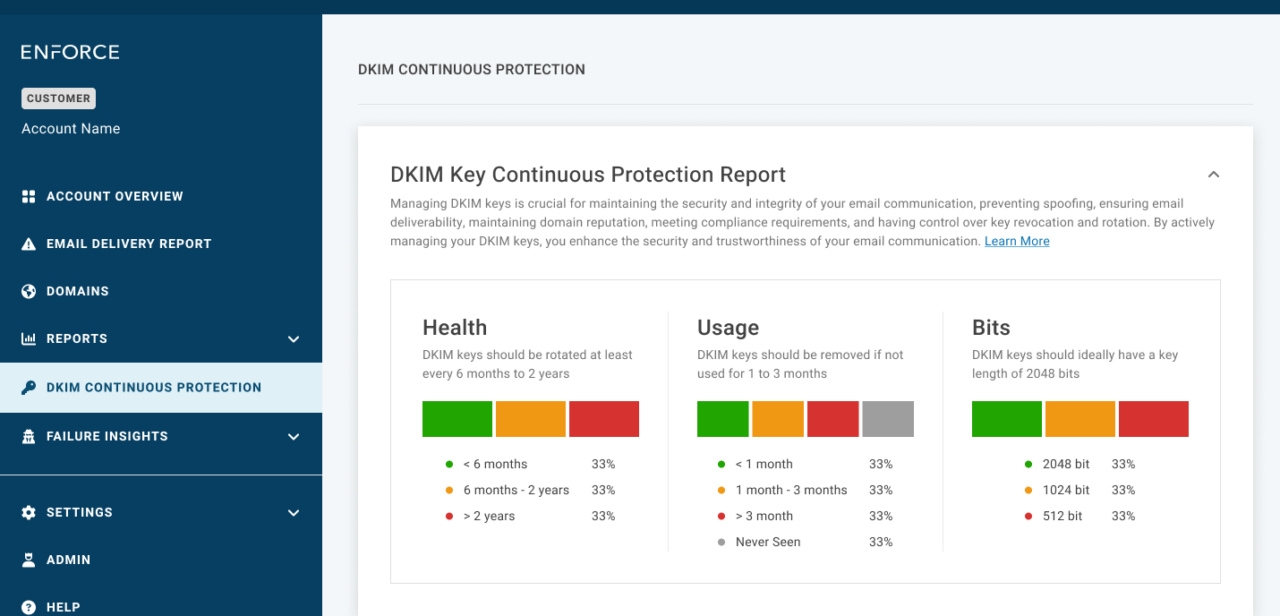
- Monitoring and reporting: You shouldn’t need a PhD to understand your DMARC reports. That’s why we provide clear, actionable insights, including our DKIM Continuous Protection Report, a powerful dashboard that tracks key age, usage, and security across all your domains. You’ll know when a DKIM key is outdated, unused, or too weak (less than 2048 bits), and get clear guidance on when it’s time to rotate or retire a key. It’s built to help you stay ahead of security best practices without the guesswork.
- Multi-domain support: Managing email authentication for multiple domains? Valimail’s got you covered.
Whether you choose to set up DKIM manually or use an automation solution like Valimail, the most important thing is that you’re taking steps to secure your email. Your future self (and your email recipients) will thank you.
Want to get a hands-on walkthrough of the Valimail platform? Schedule a demo with our email experts, and they’ll give you the grand tour.
Frequently asked questions about DKIM setup
Do I need to set up DKIM?
Yes, if you send email from your own domain. Gmail, Yahoo Mail, and Microsoft require DKIM from bulk senders, and unsigned messages are more likely to be filtered. DKIM is also one of the two ways a message can pass DMARC.
How do I know if DKIM is set up?
Send a message to a Gmail account, open “Show original,” and look for DKIM: PASS next to your own domain. You can also look up your published record with a DKIM checker.
How long does DKIM take to work?
DKIM starts working as soon as your DNS record is visible and signing is turned on. That’s often within minutes, but it can take up to 48 hours depending on your DNS host.
Is a DKIM record a TXT or a CNAME record?
It can be either. A TXT record holds your public key directly. A CNAME record points to a key your email platform hosts, which lets the platform rotate keys without changes on your side. Use the type your platform gives you.
How do I set up DKIM and DMARC together?
Set up DKIM first, along with SPF, and confirm every sender passes. Then publish a DMARC record at p=none, review the reports, and move to p=quarantine or p=reject once all your legitimate senders are aligned.